One Definition.
Every Report.
Zero Drift.
Stop rewriting the same vulnerability for the 47th time. Build your institutional knowledge once, use it forever, and watch every improvement propagate automatically across all projects and reports.
Report-Ready Writeups at Your Fingertips
Address the immediate pain of testers mid-engagement who need to document a finding quickly without sacrificing quality
Web App Writeups
1250Mixture of OWASP and CWE for web app testing
MITRE ATLAS
329Writeups for AI Pentesting, assessing LLMs
MITRE ATT&CK
455Writeups for Red Teams, TTPs
Network Infrastructure
621Writeups for internal network pentests, vuln scans, assumed breach tests
Complete Templates
Every writeup contains title, description, risk rating, attack scenario, remediation guidance, references, CVSS scoring and custom fields
Cross-Library Search
Query across all accessible libraries without pre-selecting, surfacing relevant definitions instantly through keyword matching
Hover Preview
Display full writeup details before selection, reducing false starts and ensuring the correct definition is applied
Pre-Loaded Content
2,500+ writeups from MITRE CWE, CAPEC, ATT&CK and others - included out of the box for immediate coverage of common findings
Import Your Existing Knowledgebases
Don't abandon years of institutional knowledge. Migrate seamlessly from spreadsheets, wikis, and competing tools with full field mapping support.
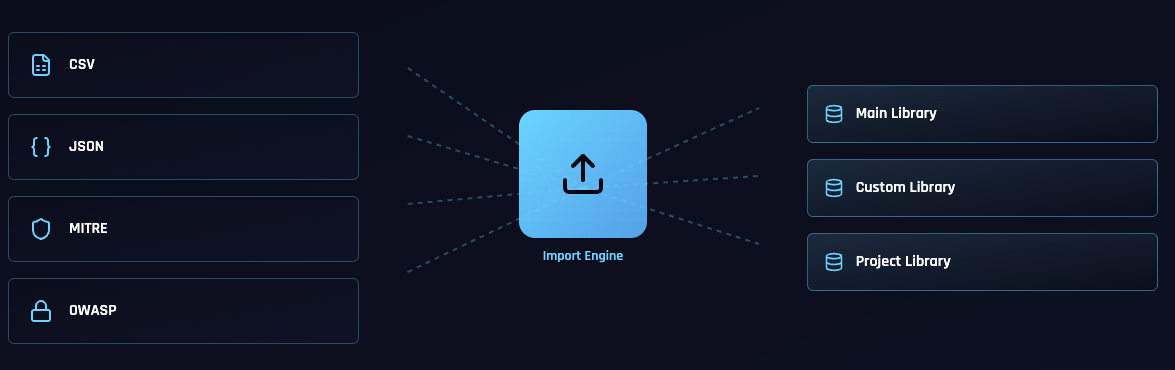
Pre-Built Imports from Industry Frameworks
MITRE Family
Methodology Frameworks
Enterprise Content PackagesReady to Deploy
Start with 2,500+ professionally curated vulnerability definitions from industry frameworks, fully mapped and ready for immediate use
Sample JSON Import Structure
{
  "title": "SQL Injection",
  "description": "An attacker can manipulate...",
  "severity": "Critical",
  "remediation": "Use parameterized queries...",
  "cwe": "CWE-89",
  "references": ["https://owasp.org/..."]
}
Access-Controlled Libraries for Every Testing Practice
Enforce need-to-know principles, support multiple customers, and enable team specialization with granular library permissions
Main Library
Organization-wideShared, comprehensive vulnerability database accessible across the organization
Imported Library
Team-levelScanner-sourced writeups from automated security tools
Project Library
Project team onlyEngagement-specific writeups visible only to project team members
Custom Libraries
Custom permissionsAdministrator-defined libraries with unlimited flexibility
Example Access Control Matrix
| Role | Main Library | Imported | Project | Custom |
|---|---|---|---|---|
| Admin | Edit | Edit | Edit | Edit |
| Senior Tester | Edit | View | Edit | View |
| Junior Tester | View | View | Edit | - |
| Client Viewer | - | - | View | - |
Multi-Team Security in Action
When Tester A on Client X's engagement searches for writeups, they see the Main Library and Client X's Custom Library, but never Client Y's proprietary content, even if both clients share common vulnerability types.
User
Tester A (Client X Team)
Can Access
Main Library, Client X Custom Library
Cannot Access
Client Y Custom Library
The Power of Linked Writeups
Unlike legacy platforms that copy writeup content at creation time, AttackForge maintains live links that propagate improvements automatically
| Capability | Copied Writeups (Legacy Platforms) | Linked Writeups (AttackForge) |
|---|---|---|
| Initial creation | Fast | Fast |
| Subsequent updates | ✕Manual sync required | Automatic propagation |
| Maintenance burden over time | ✕Increases exponentially | Remains constant |
| Consistency across projects | ✕Degrades over time | Always guaranteed |
| Unique vulnerability counting | ✕Unreliable | Accurate |
Initial creation
Copied (Legacy)
FastLinked (AttackForge)
FastSubsequent updates
Copied (Legacy)
✕Manual sync requiredLinked (AttackForge)
Automatic propagationMaintenance burden over time
Copied (Legacy)
✕Increases exponentiallyLinked (AttackForge)
Remains constantConsistency across projects
Copied (Legacy)
✕Degrades over timeLinked (AttackForge)
Always guaranteedUnique vulnerability counting
Copied (Legacy)
✕UnreliableLinked (AttackForge)
AccurateBuild Your Knowledge Once.
Use It Forever.
Every writeup created today becomes an asset that saves time tomorrow, next quarter, and for years to come. Start building your institutional knowledge now.